Founder
Sets the firm’s direction and answers personally for the standard of every engagement.
 Dallas, Texas and Luxembourg · 20 weeksMessaging Security and Operational Resilience for a Custody Bank
 Kansas City, Missouri · 16 weeksPCI DSS Scope Reduction for a Fleet Fuel-Card Issuer
 Denver, Colorado · 15 weeksSOC 2 Type II for a Legal E-Discovery Platform
StanTurton is led by its Founder, Wale Osoba, CISA, CISM, and a senior team that has delivered technology, compliance and security programs since 2016.
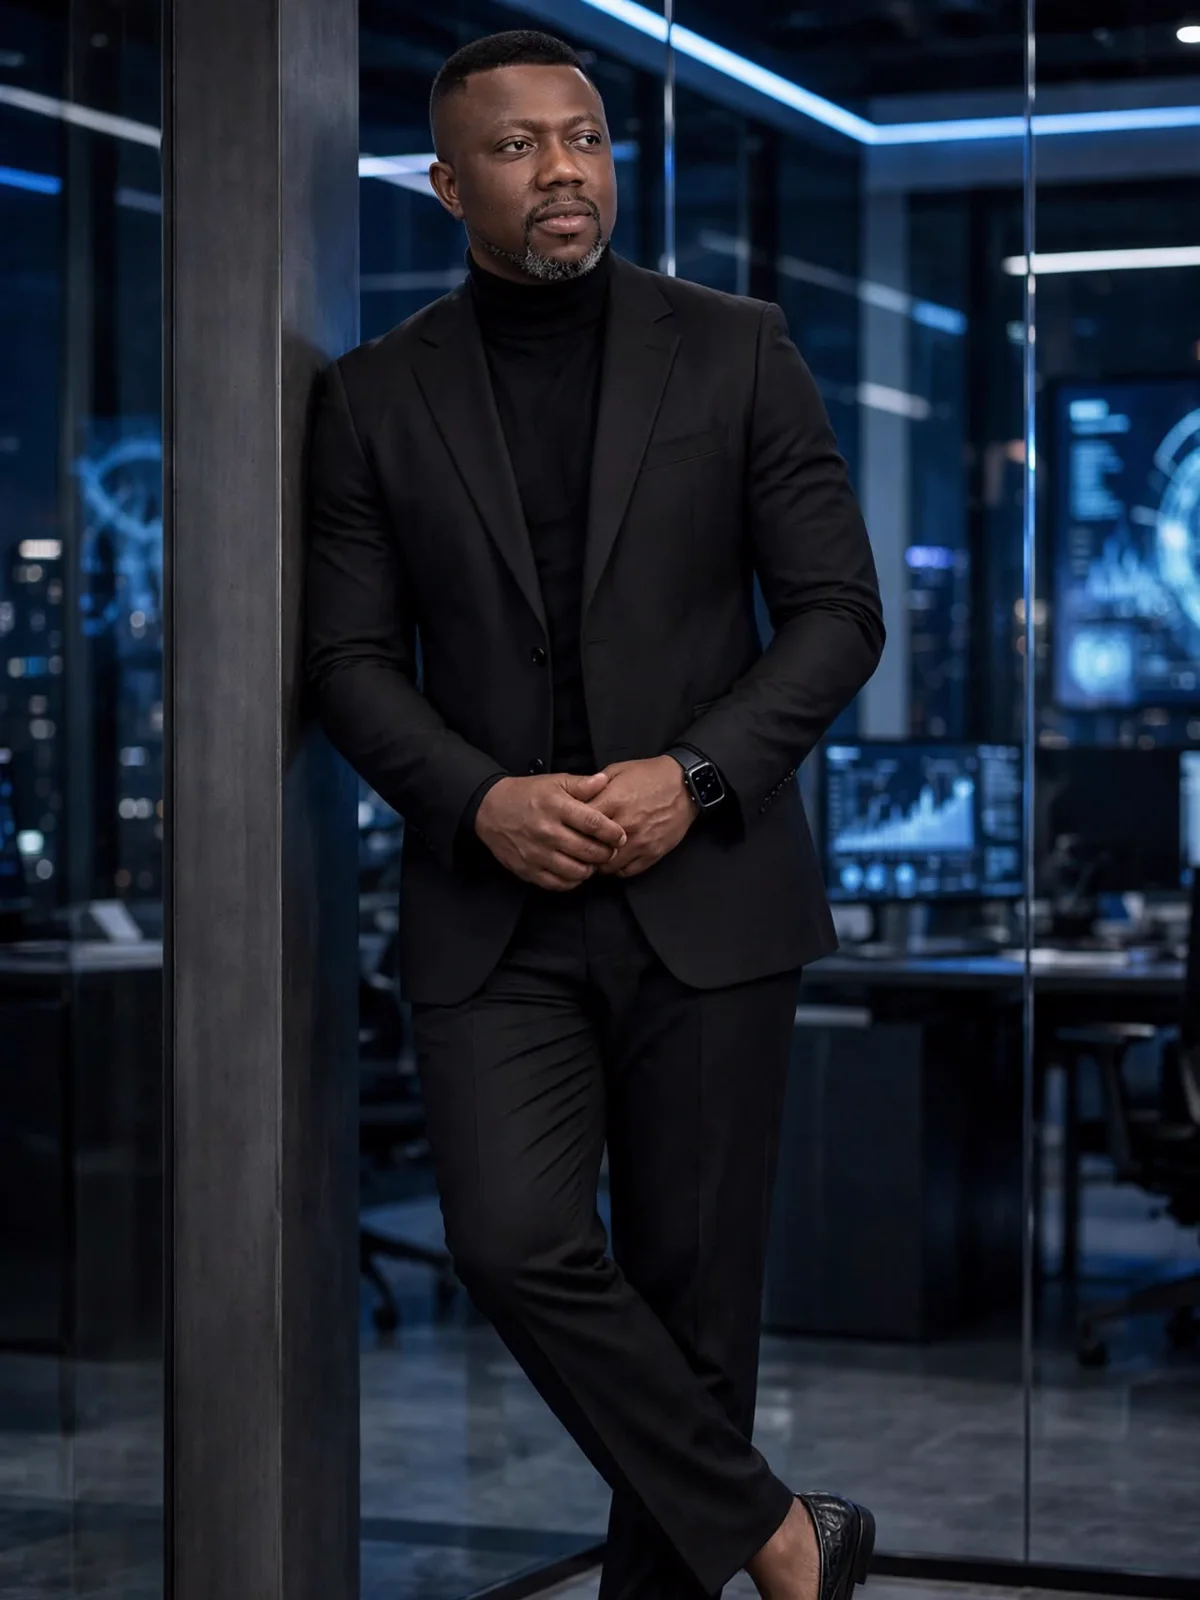
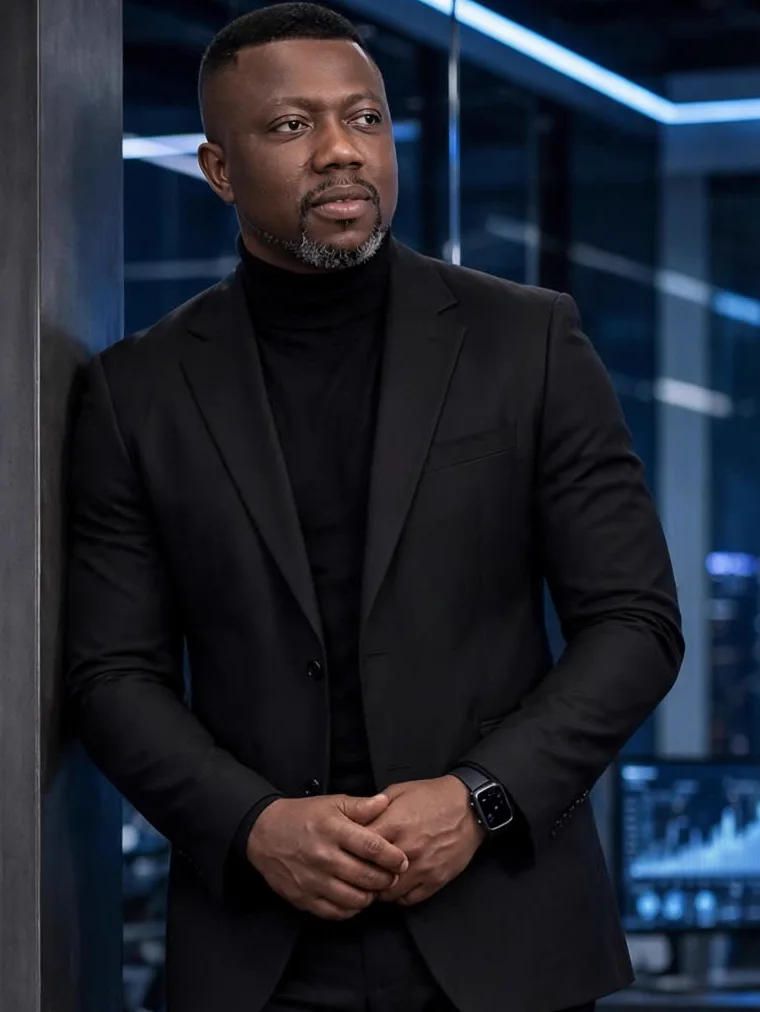
Wale Osoba builds security the way engineers build power stations: measured, load-tested and proven before anyone is asked to trust it.
Founder and Chief Executive Officer of StanTurton, Wale brings 17 years across cybersecurity, IT audit, governance, risk and compliance, and civil engineering. He founded the firm in Dallas in 2016 on one conviction: technology risk is only managed when it can be shown to an auditor, a regulator or a board, on demand.
He has worked both sides of the control. As an auditor he has evaluated internal controls, assessed third-party technology risk, reviewed cybersecurity policy and carried organizations through audits against NIST, ISO/IEC 27001 and PCI DSS. In security operations he has monitored threats, triaged alerts and investigated incidents. He knows exactly where a policy breaks when it meets a Monday morning, and he builds programs that don’t.
Before technology, Wale engineered heavy construction: power station foundations, turbine pedestals and commercial buildings, where a missed tolerance is measured in millions. That training still runs every StanTurton engagement. Milestones are planned, teams are coordinated, and problems are found while they are still cheap to fix.
As CEO, he sets the firm’s strategy around one outcome: leaders who understand their technology risk, control it, and make decisions about their IT with confidence. Clients reach him directly through the Office of the Founder.
Four principles that every StanTurton engagement inherits from its founder.
Every control is designed for the day it is tested by an attacker, an auditor or an outage. If it would crack under load, it is not finished.
An auditor’s eye at the whiteboard saves a year of rework. Every architecture we propose is checked against the questions an assessor will ask.
A control that cannot be shown working does not exist. We leave clients with proof, not promises.
The person who scopes your engagement is the person who delivers it, and the founder is one email away.
Every part of the firm has a named owner, and every engagement has a senior lead.
Sets the firm’s direction and answers personally for the standard of every engagement.
Owns PCI DSS, SWIFT CSCF and DORA methodology and delivery.
Owns AI governance, attestation readiness and cloud security engineering.
Owns penetration testing, red teaming and resilience work.
Reviews every deliverable before it leaves the firm, outside the delivery team.
Senior practitioners who scope, lead and sign off each engagement.
Every proposal names your engagement team, with the experience and certifications of each practitioner.
Any change to key people is agreed with you first.
Scoping and difficult findings are never delegated.
Every deliverable is reviewed outside the delivery team.
If something goes wrong, you reach the person who can fix it.
Your first conversation is with someone who leads engagements, not a business development team.